Digital transformation, paper and legacy systems in Japan
Part of: Japan supply-chain cyberattacks
October 17 was the day Japan's technical debt came due
SoftBank, Carsensor, 2nd STREET and GEO all went dark on one day. Shutting everything down is what technical debt leaves you with when attackers arrive.
Part 12 of a series on Japan’s cybersecurity blind spot. Start with the overview, Japan cyberattacks in 2026: what the breach wave reveals, or read the previous part, Everyone can see it. Only attackers act on it.
Update, 21 October: Recruit has disclosed that personal information tied to about 3.7 million Carsensor accounts may have leaked, Kyodo News reports. The incident has spread past Recruit: Nissan and Mitsubishi Motors suspended their used-car sites, which run on Recruit’s system. When this article was published on 20 October, Recruit had confirmed the shutdown but not the scale of any leak. The text below is as originally published.
TL;DR: On 17 October, SoftBank, Recruit’s Carsensor, Second Retailing’s 2nd STREET and GEO, and several others took whole services offline after unauthorized access or attempts at it. Shutting down was the responsible call. It was also the only call available, and that is the problem. A company that knows what it runs can cut off the part that is under attack. A company that doesn’t has one switch, and it turns everything off. Japan’s own government described this condition in 2018 and called it technical debt. Nobody has published how these systems are built, so I can’t diagnose any one company. But the circumstantial evidence is heavy, and until a company shows otherwise, expecting the worst is the reasonable position.
One day, one switch
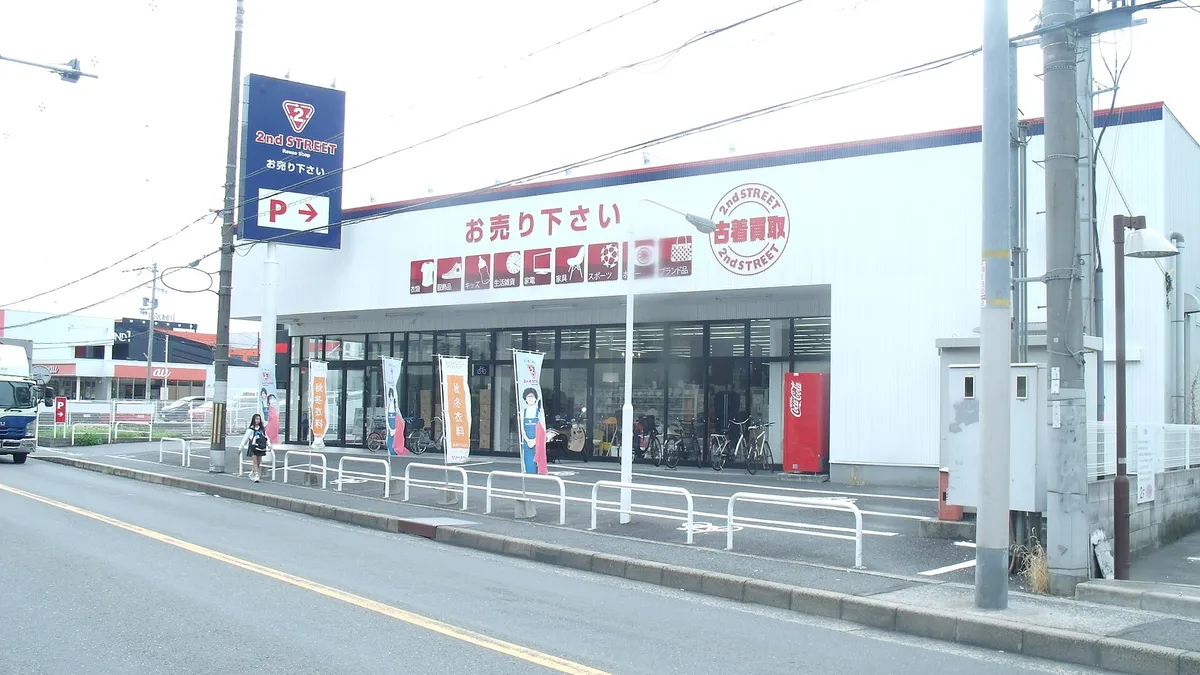
Saturday 17 October looked like a power cut moving across Japan’s consumer internet. At 8 a.m., SoftBank, one of Japan’s three big mobile carriers, stopped the web version of My SoftBank, the site customers use to manage their contracts, after detecting what Kyodo News described as attempted unauthorized access. Around 5 p.m., Recruit stopped every service connected to Carsensor, one of Japan’s largest used-car listing sites, after suspicious access from outside: the website, the app, and C-match, the system dealers use to list and price their cars. At 9 p.m., Second Retailing, the company behind the 2nd STREET reuse chain and GEO rental and game stores, switched off every app and web service across both brands and GEO Mobile, two days after confirming unauthorized access to its internal systems.
They weren’t alone. The same day, the electronics retailer Joshin restricted access from outside its network after unauthorized access, the gym-membership platform DIGYM blocked all of its sites, the Japan Football Association suspended parts of its JFA Passport app, and JETRO, the government’s trade promotion agency, took its website down. A few days earlier, Medley, which runs the @link booking and records system used mainly by obstetrics clinics, had stopped @link entirely on the night of 14 October, putting up to 787 medical institutions back on the phone.
Nobody has shown that these incidents are connected, and where the cause is public, they failed in different ways. That is not the pattern I want to point at. The pattern is the response. Company after company, faced with an intruder or a suspected one, did the same thing: it turned everything off.
FNN Prime Online’s 20 October roundup, in Japanese, of companies suspending services after unauthorized access, including SoftBank and Carsensor. Video: 不正アクセス被害相次ぐ 個人情報流出やサービス停止(2026年10月20日) from FNNプライムオンライン.
A shutdown is the right call, and a confession
I want to be fair about this. When you find someone in your systems and you don’t know what they touched, pulling the plug is responsible. Second Retailing is a good example. Its second report on 19 October says an outside security firm found no sign of suspicious connections to, or direct access of, its database servers, and no leak of personal or confidential information. It kept everything offline anyway while it strengthens security, with no restart date. That costs real money every day, across three brands, and plenty of companies would have rushed back online after a clean-looking result.
But consider what the decision says. A company whose systems are properly separated, with a current map of what runs where and what connects to what, can isolate the affected part. It shuts down one service, or one server, or one integration, and keeps the rest running while it investigates. Pulling every channel at once, with no restart date, is what you do when you can’t tell which parts are safe. Second Retailing kept its stores open, but even there, buying from customers through the app stopped, because the app sat behind the same switch.
The cost lands on people who had nothing to do with the decision. (Recruit has since disclosed a possible leak covering about 3.7 million accounts; see the update at the top.) Carsensor lists around half a million cars, and the Nikkan Jidosha Shimbun pointed out that many used-car dealers depend on it as a main sales channel and manage their listings and prices through C-match. At the clinics Medley serves, staff told FNN they were taking every booking by phone and tracking appointments by hand, and that one week of it was exhausting.
The government named this in 2018
None of this should surprise anyone who read the DX Report that a study group at METI, the Ministry of Economy, Trade and Industry, published in September 2018. It is the document that gave Japan the phrase “the 2025 digital cliff,” and most people remember only the headline: if companies didn’t replace their aging systems, the losses could reach up to about ¥12 trillion a year from 2025.
The body of the report is more useful than the headline. Citing a survey by JUAS, the Japan Users Association of Information Systems, it said about 80 percent of companies had legacy systems and about 70 percent felt those systems were holding them back. It said 80 percent of Japanese companies’ IT budgets went to keeping the current business running, and that more than 40 percent of companies spent over 90 percent that way. And it used the term directly: systems built for the short term whose running and maintenance costs keep climbing amount to paying for maintenance that was never necessary, “a kind of debt,” which it called technical debt. It warned that if this was left alone, the debt would grow, the people able to maintain the old systems would run out, and security risk would rise.
The report’s definition of the core problem is the line I keep coming back to. Legacy, it said, is the state in which a company can no longer see inside its own system and can no longer fix it with its own hands. It added that old technology alone doesn’t cause this. Systems that are maintained properly don’t easily become black boxes. The cause is management.
How the debt piles up
The METI report also explained how companies get there, and every mechanism it named shows up in this autumn’s breach wave.
The first is lost knowledge. The report noted that with lifetime employment, Japanese companies had little incentive to write down how their systems work, so the knowledge lived in the heads of particular engineers. As the generation that built the big systems retired, it said, many companies’ systems had probably already become black boxes.
The second is outsourcing without ownership. The report described companies handing even the definition of requirements to vendors wholesale, effectively asking the vendor to decide what to build. It also noted that Japan’s IT engineers sit mostly at vendors, the reverse of the pattern in the US and Europe, where the companies using the systems employ them. I made the same argument in Part 5: you outsourced the work, not the responsibility. When the vendor or the original team moves on, the understanding goes with them.
The third is that the problem stays invisible until it isn’t. The report called legacy a latent problem: as long as a system keeps working day to day, its owner doesn’t notice it has become one, and finds out only when the hardware or software reaches its limit. An intruder is another way of finding out.
The rest is in public view. In its 8 October alert on this wave, JPCERT/CC, Japan’s national computer emergency response coordination center, said attackers appear to be scanning each target for a range of known vulnerabilities, along with management lapses such as exposed configuration and backup files. Known means a fix already existed. In 2024, about 800 remote-monitoring devices at Japanese solar plants were taken over and used to relay online-banking fraud, years after the maker, Contec, first warned of the flaw. And when a company is hit, it so often can’t say for weeks how the attacker got in, or which system was reached. A company that understands its own systems can usually say that much.
What I can’t tell you
None of the companies that went dark on 17 October has published how its systems are built, and I’m not going to pretend I know. I can’t tell you that SoftBank’s or Recruit’s systems are a tangle, or that a specific update would have spared Second Retailing. SoftBank’s case, as Kyodo reported it, was an attempt, and Second Retailing found no sign that its databases were reached. A company can be well run and still choose a total shutdown out of caution.
But the circumstantial evidence points one way, and it is heavy: a government report describing the condition across most of corporate Japan, an industry still spending most of its IT money keeping old systems alive, a breach wave built on known vulnerabilities and exposed files, and a response pattern that only makes sense if nobody can tell which parts are safe. In that environment, assuming a company’s systems are a maze until it shows otherwise isn’t cynicism. It is the reasonable position. The burden is on the company, and the way to carry it is to say what happened, what was reached, and what changed.
FNN Prime Online reports, in Japanese, from obstetrics clinics handling every booking by phone after Medley shut down @link. Video: 不正アクセスで最大787医療機関で情報漏えいか 病院の予約システムダウン、すべて電話対応に 医療現場にも影響(2026年10月19日) from FNNプライムオンライン.
What paying it down looks like
The alternative isn’t exotic, and it doesn’t take a giant budget. In Part 9 I described Calil, a small team that got the Studio breach email at 10:42 and had deleted its stored form data, moved its site, and notified everyone affected by 13:40. It could do that because it knew exactly what it stored, where, and why.
For most companies, paying down technical debt starts with the ordinary stack, not a transformation program. Make a list of what you actually run: websites and the platforms under them, domains and the accounts that control them, email, cloud services, the spreadsheets doing the work of databases, and the vendor systems that hold your customers’ data. Give each one a named owner inside the company. Put updates on a schedule instead of waiting for something to break. Delete data you no longer need. And decide in advance how you would cut off one piece without turning off the rest, then try it once.
None of that is glamorous. All of it is cheaper than a weekend with every channel dark, and it’s the difference between pulling one plug and pulling the master switch.
Find out what you’re carrying
Most of the debt is internal, but some of it shows from the outside: an outdated website platform, exposed admin login pages, missing email authentication, a domain controlled by a vendor nobody has spoken to in years. The Domain Exposure Check pulls those public signals together in about a minute, with a free outline and a full report for ¥5,000 + tax. For a complete review, the external exposure check in Diagnostics covers up to three domains using the same view any customer, partner, or stranger already has, and involves no testing of your systems. If you already know the inside is a maze, Digital Baseline is where I help untangle it.
The next part, PHP2Shell: the patch is out. Do you know who installs it?, puts that debt on a deadline: a critical PHP fix that roughly half of PHP websites can’t install.
Sources
- Kyodo News via 47NEWS: SoftBank suspends My SoftBank after attempted unauthorized access (19 October 2026)
- FNN Prime Online: Unauthorized access damage spreads, with leaks and service suspensions (20 October 2026, video)
- Recruit: Notice of the temporary suspension of Carsensor-related services (updated 18 October 2026)
- Kyodo News: More data breaches reported by Japan prefectural police forces, companies (21 October 2026)
- Nikkan Jidosha Shimbun: Recruit suspends Carsensor after detecting suspicious access, no restart date
- Second Retailing: First report on unauthorized access to internal systems (17 October 2026)
- Second Retailing: Second report on the investigation of the unauthorized access (19 October 2026)
- Joshin Denki: Notice and apology regarding system disruption caused by unauthorized access (17 October 2026)
- Digisupport: Notice on unauthorized access to DIGYM
- TBS NEWS DIG: Unauthorized access at the Japan Football Association and Carsensor
- FNN Prime Online: Unauthorized access at Carsensor, and JETRO suspends its website
- Yomiuri Shimbun: Unauthorized access at Medley, patient data at up to 787 medical institutions possibly leaked
- Asahi Shimbun: Unauthorized access to a system used mainly by obstetrics clinics
- FNN Prime Online: Clinic booking systems down, all reservations by phone (19 October 2026, video)
- METI: DX Report, overcoming the 2025 digital cliff (7 September 2018, Japanese, archived copy)
- JPCERT/CC: Alert on the recent wave of unauthorized access at Japanese organizations (8 October 2026, updated 9 October)
- piyolog: Contec SolarView Compact devices hijacked and used for online banking fraud (May 2024)